Identify Security Gaps Before They Become Business Risks
A cyber-attack typically does not declare its presence until it has caused some harm. An application that is vulnerable, misconfiguration of the cloud environment, a network service exposed or any loophole in the security could be an entry point for attackers. At Rivansys, we offer Cybersecurity Assessment Services to help businesses understand their current security posture, identify weaknesses, and take practical steps to strengthen their defences.
As a technology partner who specializes in cybersecurity services, our methodology involves a combination of an assessment process as well as actionable suggestions. It is not just about identifying weaknesses but also understanding the possible business implications of any security holes.
Comprehensive Cybersecurity Assessment for Modern Businesses
Every business operates across multiple layers of technology, including websites, applications, networks, cloud infrastructure, endpoints, and business data. Our Cybersecurity audit services in India evaluate these environments to identify security weaknesses, control gaps, misconfigurations, and areas requiring improvement.
Our Cybersecurity risk assessment services in Gujarat also help organizations gain a clearer understanding of their current risks and establish priorities for improving their overall security posture.
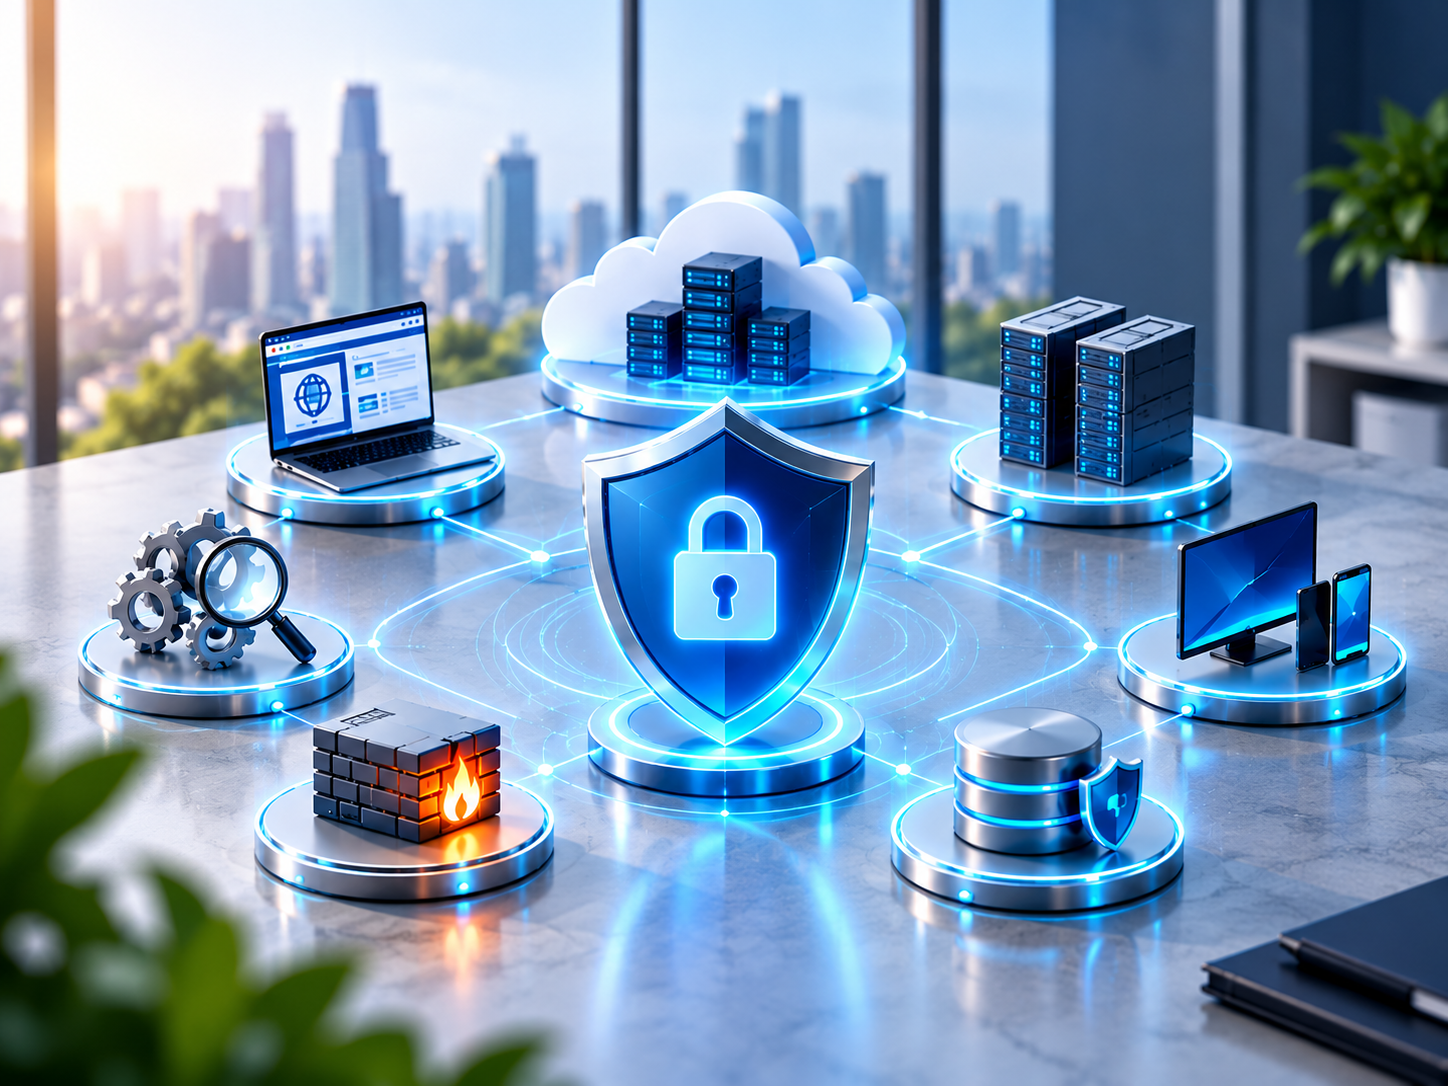
Our Cybersecurity Assessment Services
VAPT Services
Rivansys' VAPT services help in detecting security loopholes through a combination of vulnerability assessments and penetration tests before the attacker can take advantage of them. Vulnerabilities in applications, network, infrastructures, and other assets are detected, validated, and appropriate measures for their rectification are recommended.
Web Application Security Assessment
Through our Web Application Security Assessment, companies can find the vulnerabilities that may lead to unauthorized access and modification of their websites and web applications. Our team will review the authentication mechanisms, authorization controls, input validation, session handling, configuration issues, and logical flaws of your application.
Mobile Application Security Assessment
Mobile applications often handle sensitive business and customer information. Our Mobile Application Security Assessment evaluates applications for vulnerabilities across authentication, data storage, communication, API interactions, application functionality, and other critical security areas. This helps businesses identify weaknesses and improve the security of their mobile applications.
Thick Client Security Assessment
Our Thick Client Security Assessment focuses on the review of desktop-based applications dealing with processing, storage, or transmission of any sensitive information. Application behaviour, authentication procedures, data management, communication paths, configurations, and possible vulnerabilities are analysed to detect any security risks inherent in the application and its environment.
Network Security Assessment
A secure network is vital for the protection of business systems, their users, applications, and information stored on them. Our Network Security Assessment is aimed at the analysis of network architecture, available services, configurations, access rights, and possible attack vectors.
Cloud Security Assessment
As businesses increasingly rely on cloud infrastructure, misconfigurations and weak access controls can create security exposure. Our Cloud Security Assessment evaluates cloud environments, identity and access controls, configurations, workloads, data protection, and security practices. Our Cloud security assessment services in India help organizations identify risks and improve their cloud security posture.
Secure Code Review
Security vulnerabilities can originate within application source code before an application reaches production. Our Secure Code Review examines source code to identify security flaws, unsafe coding practices, authentication and authorization weaknesses, input validation issues, and other vulnerabilities. We provide actionable recommendations that help development teams address security issues earlier in the software development lifecycle.
From Findings to Actionable Security Improvements
The value of the assessment report lies in its ability to make the decision for the company on its future steps. Rivansys ranks our findings by their importance and offers practical recommendations for remediation.
Our assessments can be useful to the organization in identifying vulnerabilities, enhancing security controls, prioritizing remediation efforts, helping with compliance projects, and building a better road map for cybersecurity. The VAPT compliance services we offer in India can assist those companies that require security testing for compliance reasons.
Why Choose Rivansys?
Rivansys combines cybersecurity expertise with a practical understanding of modern business technology. Whether you need application testing, network assessment, cloud security evaluation, or a broader cyber risk assessment, our objective is to provide clear findings and meaningful next steps.