Identify Security Flaws Before Application Reaches Production
Vulnerabilities may exist within the application code much before an application is put into production. Authentication, authorization, data handling, data protection, and error handling within the coding process may have an impact on the security of the application.
Rivansys provides Secure Code Review services to identify security weaknesses at the code level and help development teams address vulnerabilities earlier in the software development lifecycle.
Comprehensive Secure Code Review
Our review concentrates on the security-critical sections of application code and analyzes how these security problems may influence application operation, data, and users.
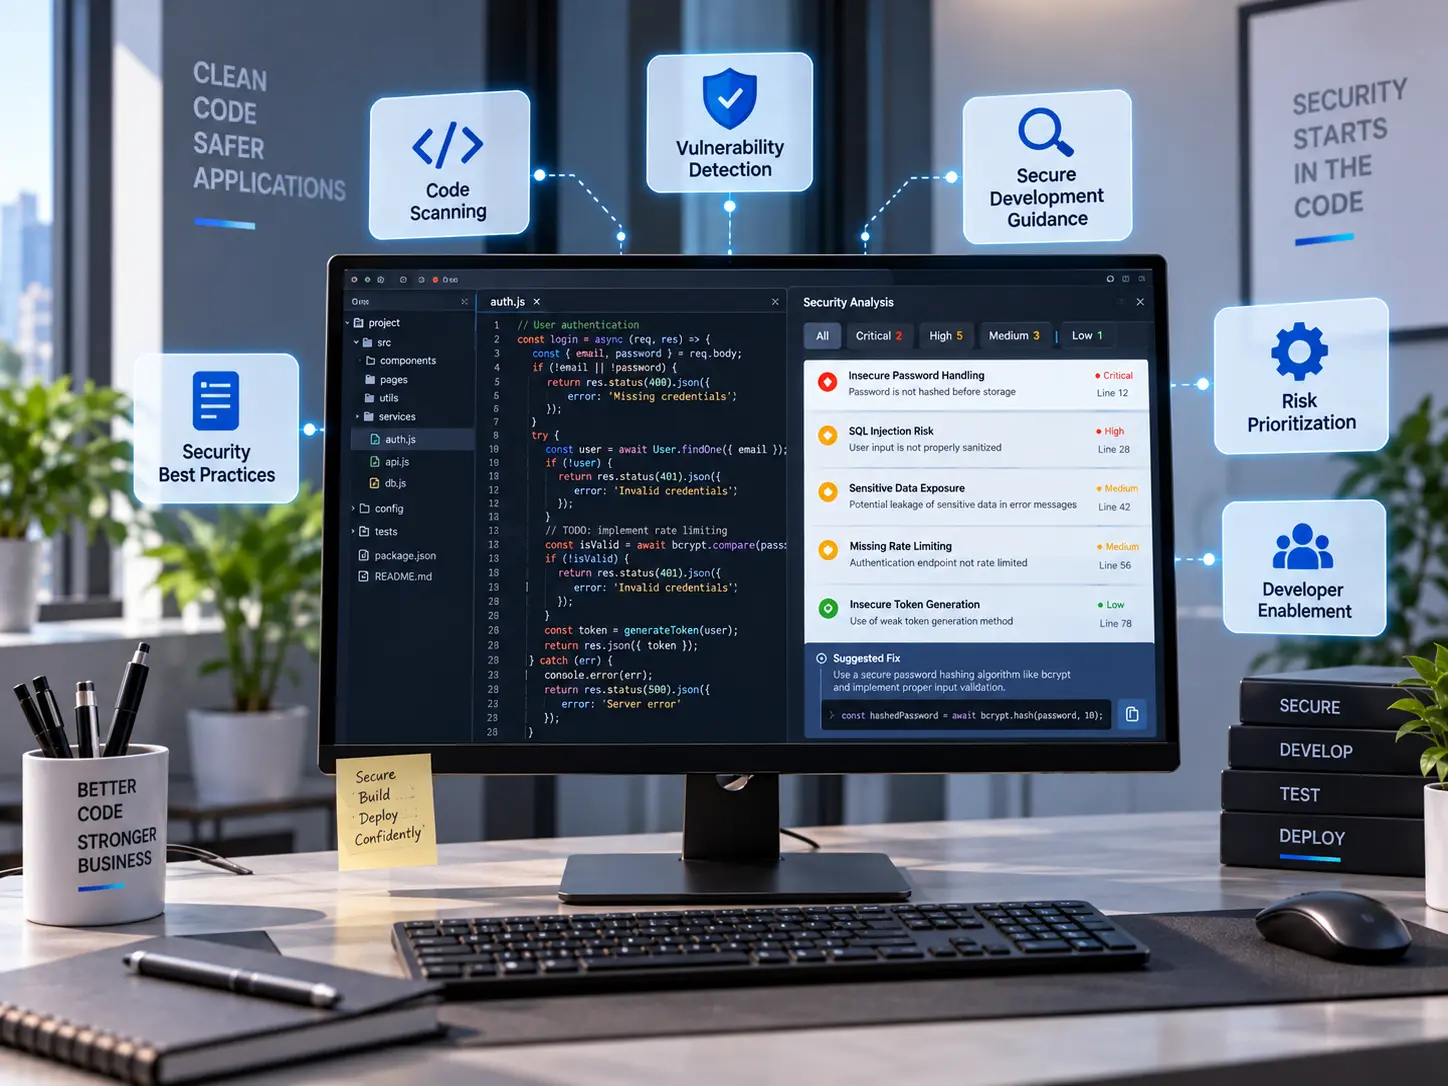
Code Review Focus Areas
Authentication & Session Logic
We review authentication logic, password handling, session management, token handling, and related controls to identify weaknesses that could allow unauthorized access.
Authorization & Access Controls
Application permissions should be enforced consistently throughout the code. We examine authorization logic to identify opportunities for privilege escalation or unauthorized access to protected functionality.
Input Validation & Injection
Improperly handled input can create serious application vulnerabilities. We examine input validation, sanitization, parameter handling, and data processing to identify potential injection and manipulation risks.
Sensitive Data & Secrets
We review how sensitive information such as credentials, tokens, personal information, and application secrets is handled within the code. This includes looking for insecure storage, unnecessary exposure, and hardcoded secrets.
Cryptography Implementation
Where cryptographic functions are used, we review their implementation and usage for security weaknesses, inappropriate handling, or insecure practices.
Error Handling & Business Logic
Detailed errors can unintentionally reveal sensitive technical information. We examine error handling and logging practices, along with security-sensitive business logic, to identify situations where application functionality could be manipulated.
Our Secure Code Review Process
1. Code & Scope Understanding
We understand the application, technology stack, repositories, modules, and security requirements within scope.
2. Automated Code Analysis
Relevant security analysis techniques are used to identify potentially vulnerable code patterns.
3. Manual Code Review
Security specialists manually examine critical areas to identify contextual vulnerabilities that automated tools may not recognize.
4. Vulnerability Validation
Findings are reviewed to assess their relevance, severity, and potential impact.
5. Remediation Guidance
The final report provides practical recommendations to help development teams address identified security issues.
What Can Secure Code Review Identify?
A secure code review may identify:
- Authentication weaknesses
- Authorization flaws
- Injection risks
- Hardcoded credentials or secrets
- Insecure data handling
- Cryptographic issues
- Sensitive information exposure
- Improper input validation
- Insecure error handling
- Business logic vulnerabilities
- Security-sensitive coding weaknesses
Why Review Code before Production?
Fixing security issues during development can reduce the complexity associated with addressing them after deployment. Code review gives development and security teams an opportunity to identify vulnerabilities earlier and incorporate stronger security practices into the application lifecycle.
Secure Code Review can also complement Application penetration testing services in India, providing a code-level perspective alongside application-level security testing.
Rivansys combines automated analysis with manual security review to examine application code in its functional and security context. Our approach is designed to provide developers with findings they can understand and act upon rather than simply producing a list of potential vulnerabilities.