Secure Your Web Applications against Real-World Threats
Web-based applications form a vital component of current business processes including customer portals and e-commerce platforms. Yet, any security weaknesses on the side of user authentication, access management, web API security, configurations or application logic leave data exposed and increase chances of data theft.
Rivansys offers Web Application Security Assessment services in order to find the existing security weaknesses in your web applications. We apply automated testing of your application security along with manual assessment of security weaknesses and provide useful recommendations for fixing those issues.
Comprehensive Web Application Security Assessment
Our security assessment addresses the issues of web application security from various angles. Instead of concentrating solely on the automated vulnerability assessment, our evaluation takes into account the interaction between application components and if vulnerabilities may be leveraged.
Our Web application VAPT services in Ahmedabad can be tailored to the application's architecture, functionality, technology stack, and business requirements.
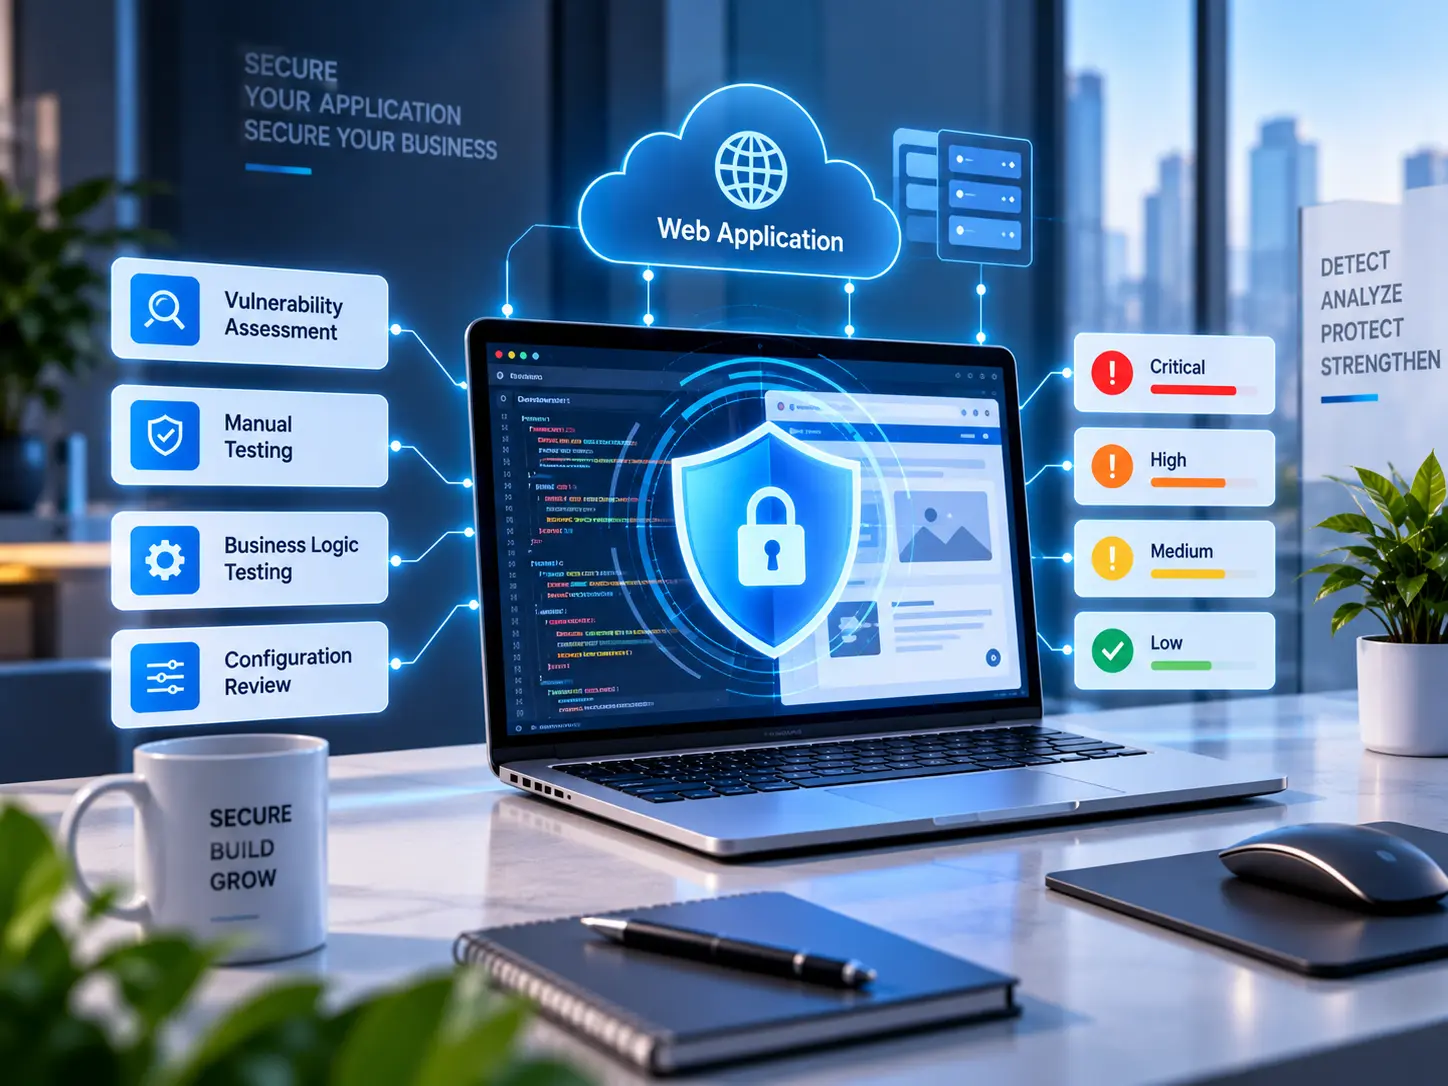
Assessment Focus Areas
Authentication & Session Security
Weak authentication mechanisms can provide attackers with opportunities to gain unauthorized access. We assess login mechanisms, password policies, session management, authentication workflows, and related controls to identify weaknesses that could compromise user accounts.
Authorization & Access Control
An authenticated user shall be granted access to functions and resources only those they have been authorized to access. Access control is evaluated to detect problems like privilege escalation, insecure direct object references, and incorrect sensitive function restrictions.
Input Validation & Injection Flaws
User input when handled carelessly by the application may pose security vulnerabilities. Our review will include evaluation of the input validation process and data handling to detect possible injection vulnerabilities and others.
API Security Assessment
Most modern web applications rely on APIs for application-to-application, application-to-service, and application-to-database communication. We analyze the API endpoint, authentication and authorization, input processing, data exposure, and other associated control points to find any potential security gaps with the API.
Business Logic Testing
All security vulnerabilities cannot be found via automated scanning. Our security experts perform a review of business processes and application logic that may be exploited to produce unwanted results.
Configuration & Security Controls
Application and server configurations can significantly influence the overall security posture. We review relevant security configurations, headers, exposed services, error handling, and other controls to identify unnecessary exposure and security weaknesses.
Our Web Application Security Assessment Process
1. Scope & Application Discovery
We begin by understanding the application's functionality, architecture, user roles, technologies, and authorized testing scope.
2. Automated Security Testing
Appropriate security tools are used to identify potential vulnerabilities and areas requiring deeper investigation.
3. Manual Security Testing
Our specialists manually validate findings and test application behavior, authentication, authorization, APIs, business logic, and other critical components.
4. Vulnerability Validation
Potential findings are analyzed to determine their actual significance and reduce false positives.
5. Detailed Reporting
We provide a structured report containing identified vulnerabilities, severity, potential impact, affected areas, and remediation recommendations.
What Can a Web Application Assessment Identify?
A comprehensive assessment may help identify security weaknesses involving:
- Authentication & session management
- Authorization & access controls
- Injection vulnerabilities
- Sensitive data exposure
- API security
- Security misconfigurations
- Input validation flaws
- Business logic vulnerabilities
- Error handling issues
- Server configuration risks
The exact testing scope depends on the application's architecture, functionality, technology stack, and engagement requirements.
Why Web Application Security Testing Matters
A vulnerable web application can affect more than technical infrastructure. Security weaknesses may expose customer information, business data, credentials, intellectual property, or critical functionality.
Regular security assessments provide organizations with greater visibility into application-level risks and help development and security teams address weaknesses before they become exploitable incidents.
For organizations looking for Application penetration testing services in India, a detailed web application assessment can also provide valuable insight into how application vulnerabilities may behave under controlled attack scenarios.
Why Choose Rivansys?
Rivansys combines structured cybersecurity assessment methodologies with practical security testing. We focus on identifying meaningful weaknesses rather than generating large volumes of unverified findings.
Our approach provides technical teams with actionable remediation guidance while giving business stakeholders a clearer understanding of application security risks.
Whether you are assessing an existing application, preparing for a major release, or validating security after significant changes, Rivansys can help you evaluate your web application's security posture.