Protect Mobile Applications Against Emerging Security Threats
Mobile applications have become an integral part of interaction between organizations and their customers, employees, and online services. On the other hand, mobile applications are capable of handling confidential credentials, personal information, payment data, enterprise data, and communication with APIs, thus becoming part of an organization's attack surface.
Rivansys offers Mobile Application Security Assessment that can help uncover vulnerabilities in mobile applications and the infrastructure surrounding them. Our security assessment service will allow us to automatically analyze the application and conduct a security test to highlight vulnerabilities.
Comprehensive Mobile Application Security Assessment
Our assessment evaluates the mobile application from multiple security perspectives, including application functionality, authentication, data storage, communication, APIs, and security configurations.
Our Mobile application VAPT services in India can be tailored to Android, iOS, and other supported mobile application environments based on the application's architecture and testing requirements.
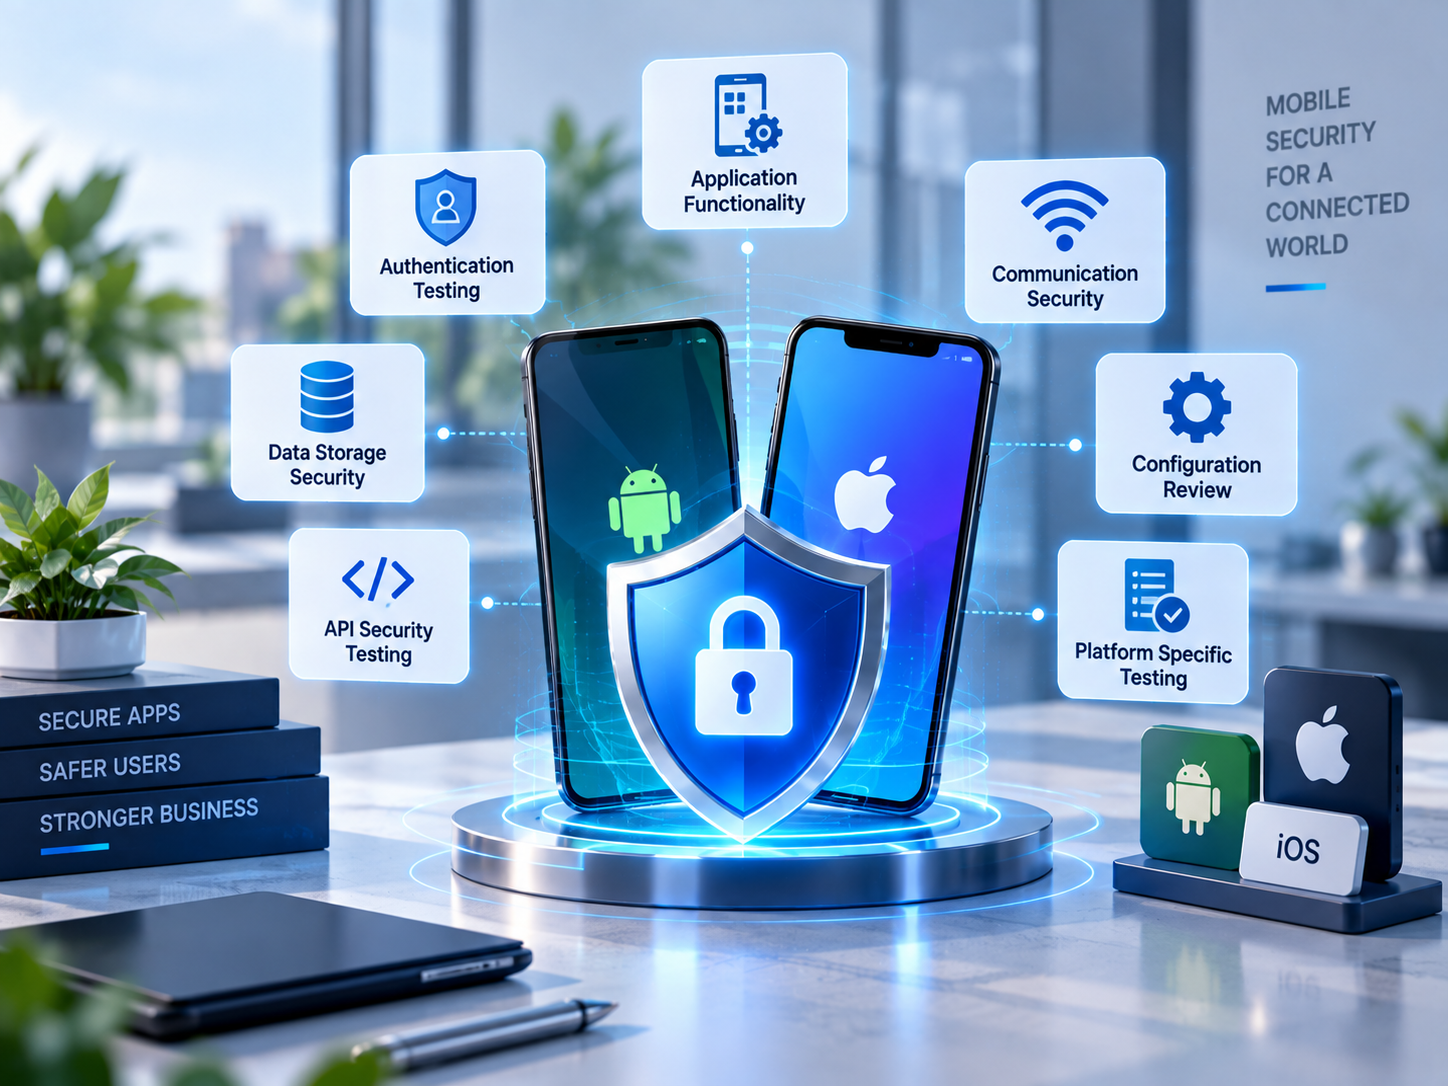
Assessment Focus Areas
Authentication & Account Security
Mobile applications often provide access to sensitive user accounts and business functionality. We assess authentication mechanisms, password controls, session handling, account management, and related security controls to identify weaknesses that could enable unauthorized access.
Authorization & Access Control
Good authorization ensures that users have access to only those features and data that are authorized based on their roles. Authorization controls and application flows are reviewed to detect cases of privilege escalation, unauthorized feature access, and other access control weaknesses.
Data Storage Security
Mobile apps can hold credentials, tokens, personally identifiable information, or any other kind of sensitive data within local storage. We analyze available storage mechanisms and the security surrounding them to find vulnerabilities leading to unnecessary exposure of sensitive information.
Data Transmission & Communication
Applications frequently communicate with backend systems and APIs. We assess communication channels, encryption mechanisms, certificate validation, and related controls to identify weaknesses that could expose information during transmission.
API Security Assessment
Mobile applications commonly depend on APIs for authentication, data retrieval, transactions, and business functionality. Our assessment examines API authentication, authorization, input handling, data exposure, and other relevant controls to identify weaknesses that could affect the mobile application ecosystem.
Application Logic & Platform Controls
Some security issues arise from request processing logic rather than single technical flaws. Our specialists assess application workflows, business logic, platform configurations, insecure settings, and debugging-related risks.
Our Mobile Application Security Assessment Process
1. Scope & Application Discovery
We begin by understanding the application's functionality, architecture, supported platforms, APIs, user roles, and authorized testing requirements.
2. Automated Security Analysis
Appropriate tools and techniques are used to identify potential vulnerabilities and security weaknesses requiring further investigation.
3. Manual Security Testing
Our security specialists perform manual testing to validate findings and evaluate application behavior across authentication, authorization, data handling, APIs, communication, and business logic.
4. Vulnerability Validation
Potential vulnerabilities are analyzed to determine their relevance, severity, and potential impact while reducing false positives.
5. Reporting & Remediation Guidance
The final assessment report provides clear details about identified vulnerabilities, affected components, potential impact, severity, and recommended remediation measures.
What Can a Mobile Application Assessment Identify?
Depending on the application and assessment scope, testing may identify weaknesses involving:
- Authentication & session management
- Authorization & access controls
- Insecure local data storage
- Weak encryption or data protection
- Insecure network communication
- API vulnerabilities
- Input validation flaws
- Application logic issues
- Security misconfigurations
- Platform-specific security controls
The assessment scope can be adapted according to the application's technology, business functionality, and security requirements.
Why Mobile Application Security Testing Matters
The security of a mobile application is not determined by just the software which is installed in the user's device. There are many other things involved in securing an application, including API integration, the backend service, database, authentication systems, and other third-party products.
Performing security assessments is a way of early identification of vulnerabilities, validation of existing control measures, and providing information to the developers to improve application security.
For organizations seeking Mobile Application VAPT Services in India, a structured security assessment can provide valuable visibility into both application-level and supporting security risks.
Why Choose Rivansys?
Rivansys follows a pragmatic and threat-driven approach for mobile application security assessments. Our testing is done using automation and manual testing to determine vulnerabilities instead of just following the outputs of the automation tools.
Our reports include detailed findings along with actionable recommendations which can help your security and IT teams focus on addressing vulnerabilities within the mobile applications.